How to check a PDF's digital signature: a step-by-step guide
Opdateret 2. oktober 2026
Denne vejledning findes endnu ikke på dansk, så den vises på engelsk. Selve værktøjet fungerer på dansk.
A signed contract, an e-invoice, a land-registry extract: Verify PDF Signature checks every digital signature in a PDF - that the signed content is unchanged, that the signature matches its certificate, what was added afterwards, who issued the certificate and whether that provider is on the EU trusted lists or the U.S. Federal PKI. It makes no file and costs nothing from the daily limit. It all happens in your browser; nothing is uploaded.
Prøv gratis, uden konto: dine filer forlader aldrig din enhed.
Kort fortalt
- Drop the signed PDFs on the page, or press Add files.
- Each file is checked as it arrives; the list says intact, needs a look or not valid.
- Read the card of each signature in the middle.
- If the file changed after signing, save the version that was signed.
Add the files
Drop the PDFs anywhere on the page, or press Add files. Every file is checked the moment it arrives. The list gives a one-word verdict - intact, needs a look, not valid, or no digital signature - and the middle shows the selected file's report, with a card for every signature.
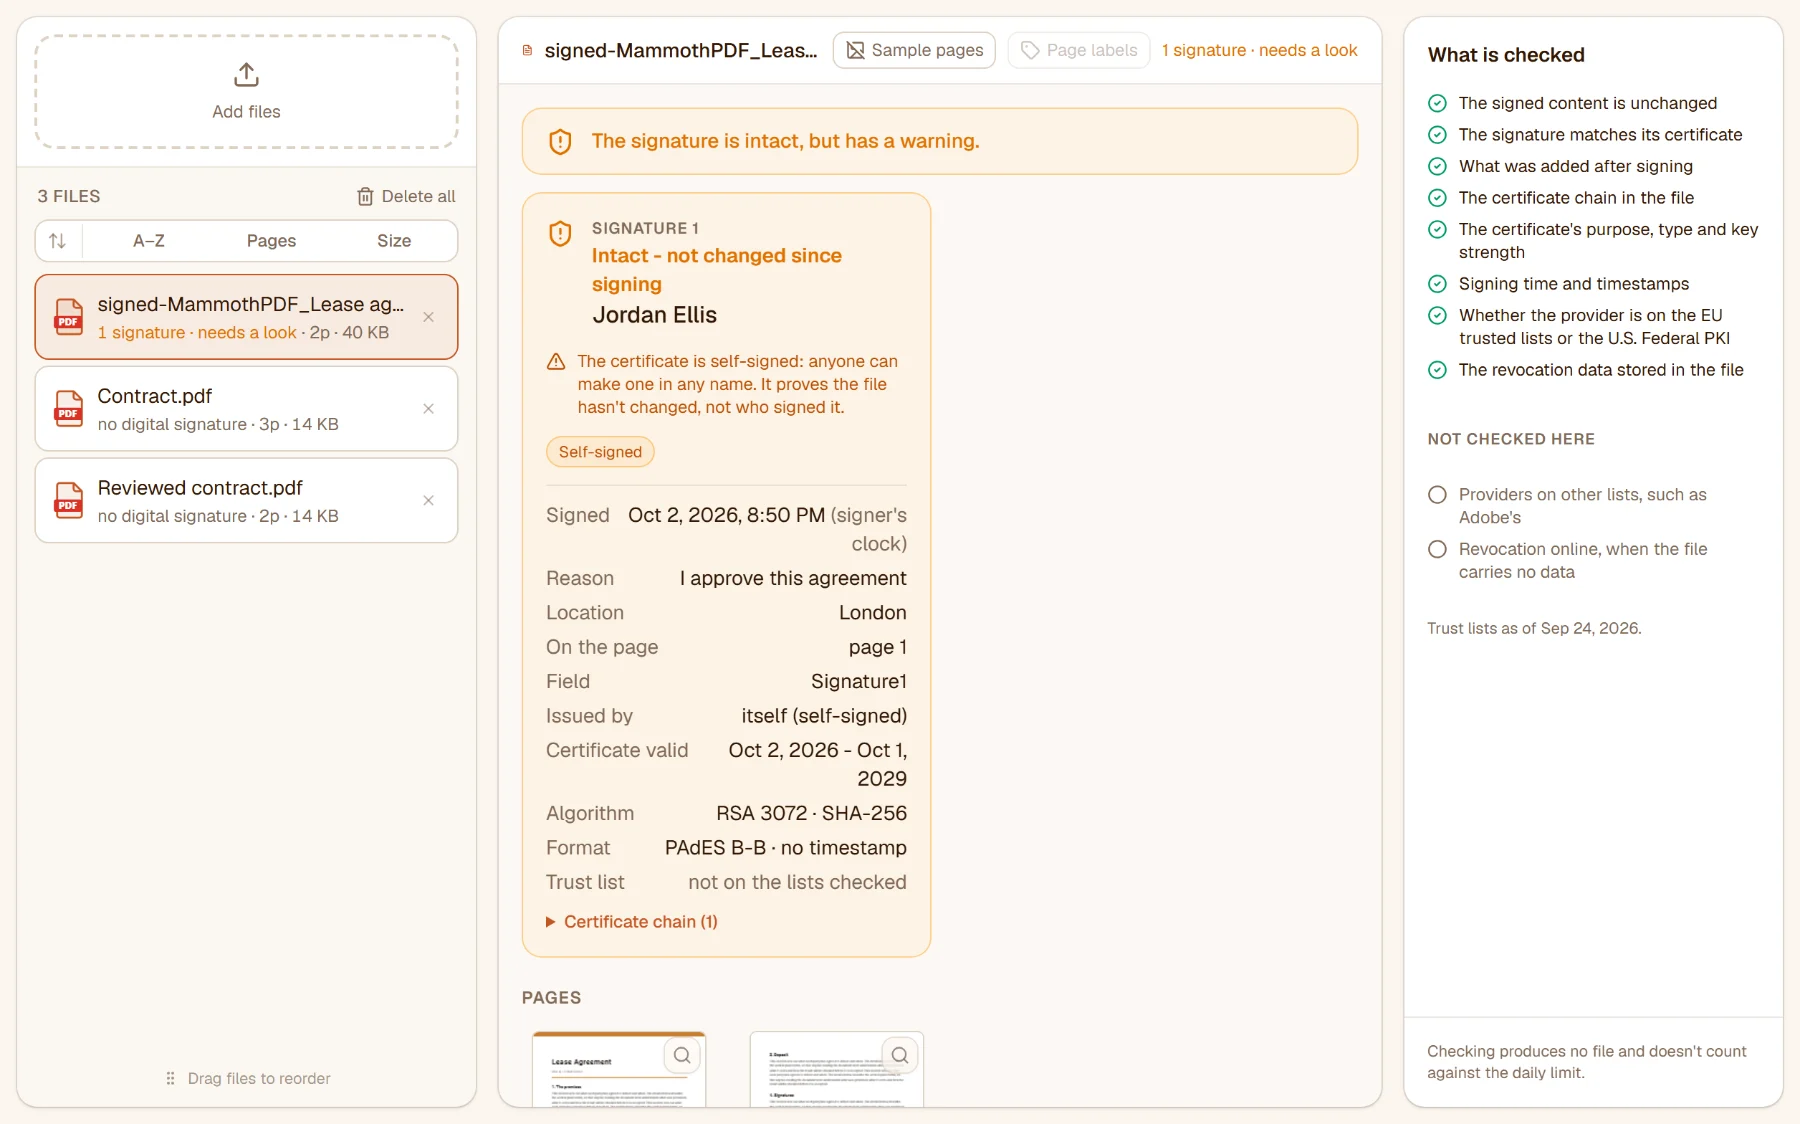
Read the signature card
At the top of a card is the verdict - "Intact - not changed since signing" is what you hope for - and the signer's name. Under it: when it was signed (and by whose clock), the reason and place, the page the signature sits on, who issued the certificate and how long it is valid, the algorithm, the format and level (PAdES B-B to B-LTA), the trust list, and the certificate chain.
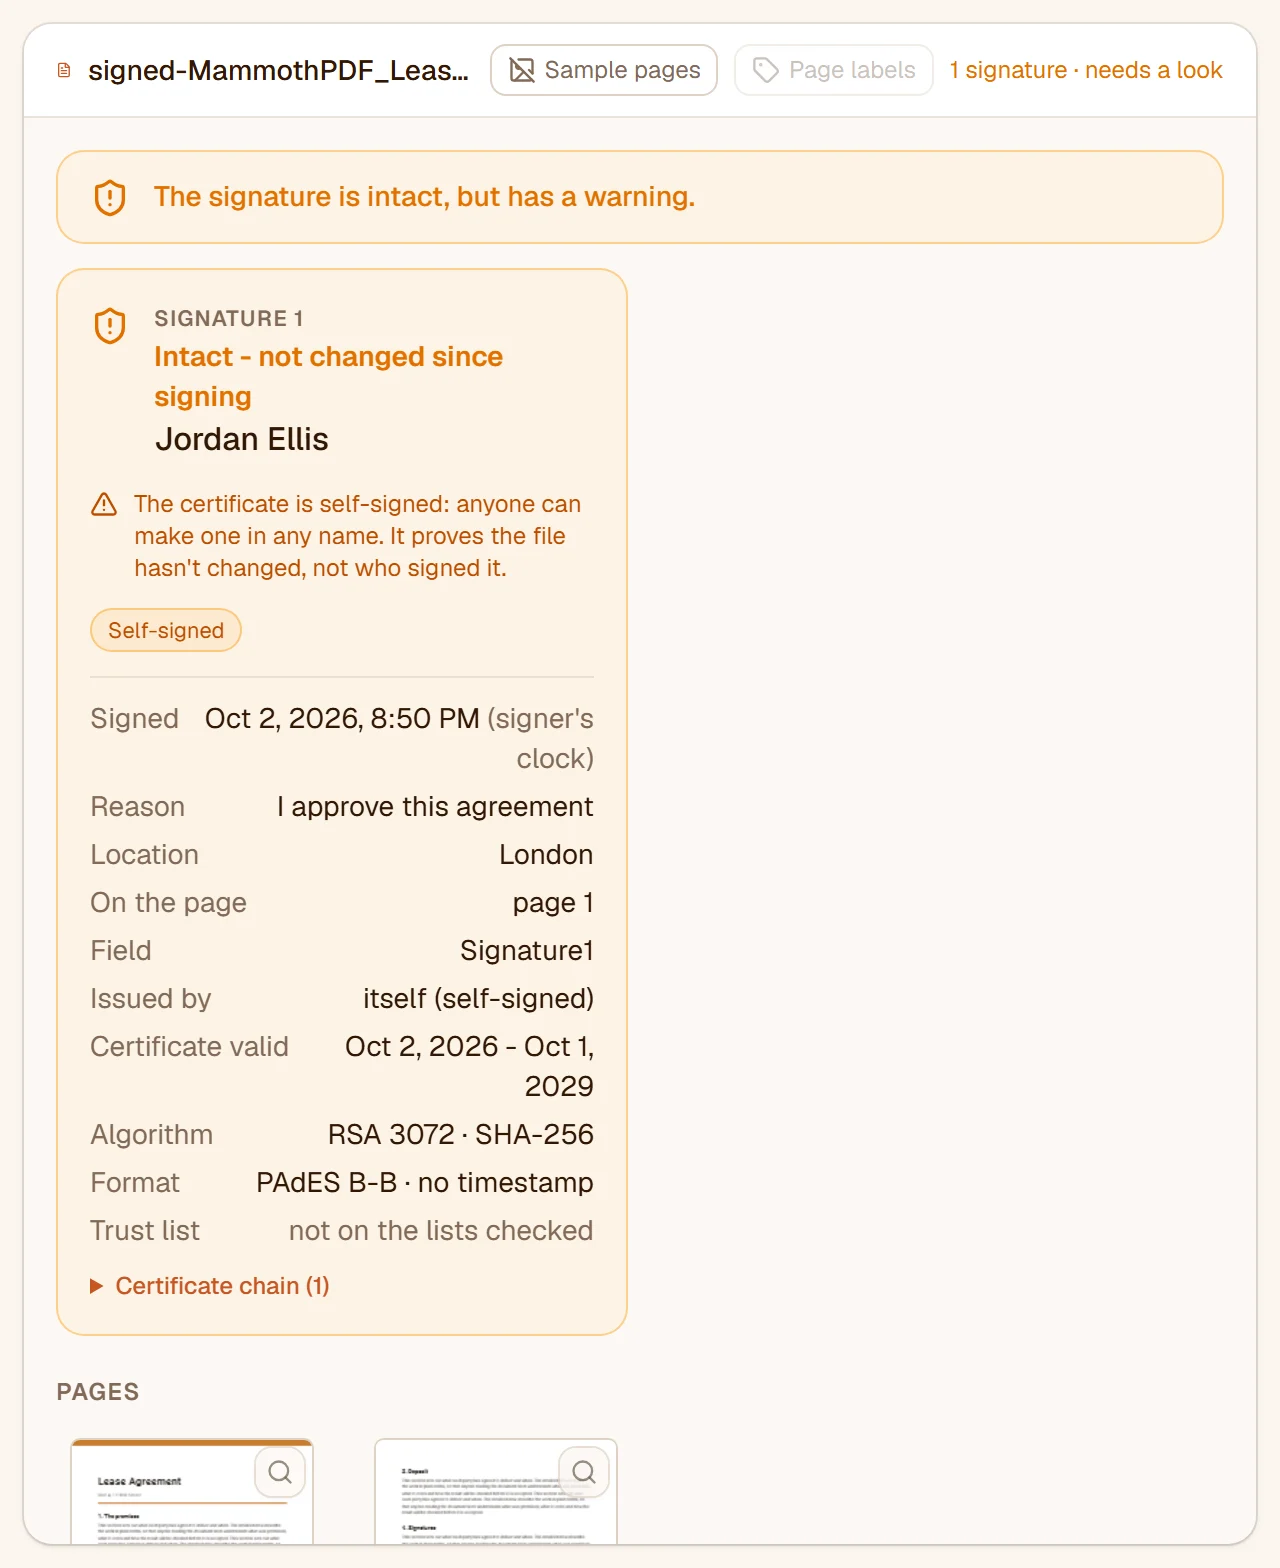
- Warnings say what to look at: a self-signed certificate, a certificate that wasn't valid at the signing time, a weak hash, content added after signing that no signature covers.
- Trust list: a provider on an EU trusted list (with its status at the signing time) or the U.S. Federal PKI is named; a qualified electronic signature or seal is labelled as such.
- Revocation: what the file itself carries - OCSP answers and revocation lists - is checked.
When the file changed after signing
If content was changed after a signature, the card offers Save the signed version - the file exactly as it was when that signature was made - and Compare with the current version, which opens the two side by side in Compare PDFs to show what changed.
Not checked here: providers that are only on other lists, such as Adobe's, and revocation online when the file carries no data. The rail lists what is and isn't checked.
Limits
Checking makes no file and doesn't count against the daily limit, with or without an account.
What next?
- Sign a document yourself? Digitally Sign PDF.
- See what changed after signing? Compare PDFs.
- Everything else the file holds? Inspect PDF.
Klar til at prøve?
Prøv gratis, uden konto: dine filer forlader aldrig din enhed.
Flere vejledninger
- How to merge PDF files: a step-by-step guideCombine PDFs, images and Office files into one PDF in your browser: order the files, add separator pages, a contents page and bookmarks, interleave two-sided scans.på engelsk
- How to split a PDF into several files: a step-by-step guideCut a PDF into separate files in your browser: at the pages you choose, every N pages, into equal parts, one file per page, or into parts small enough to e-mail.på engelsk
- How to rotate PDF pages: a step-by-step guideTurn the pages of a PDF in your browser: one page or many, by quarter turns or any angle, in several files at once - and save it so it stays turned.på engelsk
- How to mirror PDF pages: a step-by-step guideFlip PDF pages horizontally or vertically in your browser - a page scanned from the back of a transparency, a print that needs mirror-writing - for one page, some or every file at once.på engelsk
- How to straighten a crooked PDF scan: a step-by-step guideLevel a scanned PDF whose pages went in at a slant, in your browser: every page's tilt measured on its own, corrected in place, with a hand-set angle where you want one.på engelsk
- How to auto-rotate PDF pages upright: a step-by-step guideFind the sideways and upside-down pages of a scanned PDF and turn each upright, in your browser - detected page by page, checked on the thumbnails, saved without loss.på engelsk
- How to delete pages from a PDF: a step-by-step guideRemove pages from a PDF in your browser: mark them on the thumbnails, by number or with quick-selects such as every even page - in one file or many, nothing uploaded.på engelsk
- How to change the page size of a PDF: a step-by-step guidePut every page of a PDF on A4, Letter, A3, A5 or a custom size in your browser, or shrink the content on the page it has - vector text stays sharp, links and form fields stay in place.på engelsk
- How to reorder PDF pages: a step-by-step guideRearrange the pages of a PDF in your browser: drag the thumbnails, move a selection to the front, the back or in front of any page, or reverse the order - nothing uploaded.på engelsk
- How to reverse the page order of a PDF: a step-by-step guideTurn the page order of a PDF back to front in your browser - a scan fed in last page first, or only a chosen run of pages - in one file or many at once.på engelsk
- How to extract pages from a PDF: a step-by-step guideTake the pages you need out of one or more PDFs in your browser: pick them on the thumbnails or by number, save them as one PDF, one per file, per range or per page.på engelsk
- How to crop a PDF: trim the margins step by stepTrim the white margins of PDF pages in your browser, or cut them to a frame you draw - one frame for every page, odd and even pages apart, or each page its own.på engelsk
- How to print several PDF pages on one sheet, or make a booklet: a step-by-step guideLay 2, 4, 6, 8, 9 or 16 PDF pages out on one sheet, or arrange a PDF as a folded booklet, in your browser - the sheets previewed exactly as they will be saved, text kept sharp.på engelsk
- How to edit a PDF: rewrite its text, add text, pictures, tables and pages - a step-by-step guideEdit a PDF in your browser like a word processor: rewrite the document's own paragraphs, format a selection, add text boxes, pictures, shapes, tables, links, comments and form fields, add and delete pages, find and replace. Nothing is uploaded.på engelsk
- How to sign a PDF online: a step-by-step guideSign a PDF in your browser: draw, type or upload your signature, place it on the page, add a second signer, put it on every page - nothing is uploaded.på engelsk
- How to fill in a PDF form: a step-by-step guideType into a PDF form's fields right on the page in your browser - text, check boxes, lists, choices - then save it filled in, or locked so nobody can change it.på engelsk
- How to add a watermark to a PDF: a step-by-step guideStamp a text or logo watermark on PDF pages in your browser: diagonal or in a corner, repeated over the page, with the size and opacity you choose - nothing uploaded.på engelsk
- How to add page numbers to a PDF: a step-by-step guideNumber the pages of a PDF in your browser: choose the pages, the position and the margin, skip the cover, start from any number, write "Page 3 of 12" in your own style.på engelsk
- How to change or remove PDF metadata: a step-by-step guideEdit a PDF's title, author, subject, keywords, application and creation date in your browser - or clear them all before the file leaves the house - written so every viewer shows the same.på engelsk
- How to flatten a PDF: a step-by-step guideBurn form fields, comments, highlights and stamps into the page of a PDF in your browser - or take them off - so the file looks the same in every viewer and can no longer be changed.på engelsk
- How to compare two PDF versions: a step-by-step guideSee what changed between two versions of a PDF in your browser - the words removed, added and replaced, marked on the two pages side by side, and a report to keep. Nothing is uploaded.på engelsk
- How to make a PDF smaller: compress it step by stepShrink a PDF in your browser: pick a compression level, see the size before and after, compress several files in one go - text stays sharp, nothing is uploaded.på engelsk
- How to make a PDF open fast on the web (Fast Web View): a step-by-step guideLinearize a PDF in your browser so a reader shows its first page while the rest is still downloading - for a PDF served from a website or a link. The pages stay exactly as they are.på engelsk
- How to remove hidden data from a PDF: a step-by-step guideTake out what a PDF carries beside its pages - metadata, attached files, embedded video, scripts, comments, thumbnails - in your browser, before the document leaves the house. The pages stay as they are.på engelsk
- How to repair a damaged PDF that won't open: a step-by-step guideFix a PDF that a reader refuses to open - a download that was cut off, a file with a broken table of contents - in your browser. Each file is checked as it arrives, and you see what was wrong and what came back.på engelsk
- How to see what is inside a PDF: a step-by-step guideInspect a PDF in your browser: its pages and sizes, what makes it big, its images and their resolution, its fonts, the hidden data it carries - and which tool would help next. Nothing is uploaded.på engelsk
- How to remove blank pages from a PDF: a step-by-step guideFind and delete the empty pages a duplex scan leaves behind, in your browser: every page measured, the blank ones marked for you to check, a scanner's dark edge ignored.på engelsk
- How to remove duplicate pages from a PDF: a step-by-step guideFind the pages that repeat an earlier one - a sheet fed through the scanner twice, an attachment merged in again - and delete them in your browser, after checking every mark on the thumbnails.på engelsk
- How to redact a PDF: remove names and numbers for goodBlack out names, e-mails, phone and account numbers in a PDF in your browser - the content is deleted from the file, not just covered. Search, patterns or drag.på engelsk
- How to password-protect a PDF: a step-by-step guidePut a password on a PDF in your browser with AES-256 encryption, and choose whether readers may print, edit or copy - the file and the password never leave your device.på engelsk
- How to remove a password from a PDF: a step-by-step guideUnlock a PDF in your browser: take the password off a file you know the password of, or lift restrictions that block printing and copying - nothing is uploaded.på engelsk
- How to digitally sign a PDF with a certificate: a step-by-step guideSign a PDF with your certificate (.p12 / .pfx) in your browser, or with one made on the spot - a real digital signature that proves the document hasn't changed since. Free, nothing uploaded.på engelsk
- How to turn images into a PDF: a step-by-step guideMake a PDF from JPG, PNG and other photos in your browser: put them in order, pick the page size and margin, one image per page or several on a sheet.på engelsk
- How to convert PDF pages to JPG or PNG images: a step-by-step guideSave the pages of a PDF as JPG, PNG or WebP images in your browser: choose the pages, the format, the quality and the resolution - nothing is uploaded.på engelsk
- How to extract images from a PDF: a step-by-step guideSave every picture embedded in a PDF as a JPG or PNG file, in your browser - a JPEG comes out as the very JPEG in the file, with no second loss of quality; icons and rules can be left out.på engelsk
- How to convert a PDF to grayscale: a step-by-step guideTurn a colour PDF black-and-white in your browser for printing or archiving - text stays sharp and selectable, pictures and gradients turn grey, nothing is uploaded.på engelsk
- How to make a scanned PDF searchable with OCR: a step-by-step guideRecognise the text of a scanned PDF in your browser and add a searchable, selectable text layer - the language detected for you, the scan itself untouched, nothing uploaded.på engelsk
- How to extract the text of a PDF to a .txt file: a step-by-step guideSave the text of a PDF as a plain .txt file in your browser - as paragraphs that reflow, or line by line as on the page - for some pages or all, with the preview on screen before you save.på engelsk
- How to convert a PDF to Word: a step-by-step guideTurn a PDF into an editable Word document in your browser: keep the page as it looks, or get the text as paragraphs or lines - choose the pages, nothing is uploaded.på engelsk
- How to convert the tables of a PDF to Excel: a step-by-step guideTurn the tables in a PDF into an Excel workbook (.xlsx) in your browser - numbers as real numbers that add up, the tables checked on screen before you save.på engelsk
- How to convert a PDF to PowerPoint: a step-by-step guideTurn every page of a PDF into a PowerPoint slide (.pptx) in your browser - the slide looks like the page, and every word stays editable text in a box of its own.på engelsk
- How to convert Word to PDF: a step-by-step guideTurn Word documents (.docx) into PDFs in your browser - text, lists, tables, pictures, headers and footers kept, several documents at once, nothing uploaded.på engelsk
- How to convert an Excel workbook to PDF: a step-by-step guideTurn an Excel workbook (.xlsx) into a PDF in your browser, every sheet paged the way Excel prints it - no Excel needed, nothing uploaded.på engelsk
- How to convert a PowerPoint presentation to PDF: a step-by-step guideTurn a PowerPoint deck (.pptx) into a PDF in your browser, one page per slide at the slide's size - no PowerPoint needed, nothing uploaded.på engelsk